Written by: Luis Teran, Co-founder, CEO, TenantEvaluation | Last updated: September 15, 2026
Key Takeaways For HOA Screening Compliance
- Secure applicant data collection for HOA screening compliance starts with collecting only what screening requires, restricting access through role-based controls with MFA, and separating decision records from sensitive screening files.
- The two-file record architecture offers a practical framework: board members access only the decision file while the sensitive screening file containing PII stays with authorized screeners.
- HOAs need role-based access control, prompt access revocation when board members rotate off, and written security clauses in screening vendor contracts that cover encryption standards and breach notification requirements.
- Written retention and destruction schedules are essential. Records stay only as long as there is a documented business or legal need, then the HOA securely deletes them using methods that render data unrecoverable.
- TenantEvaluation provides a platform that turns these compliance requirements into daily practice with built-in two-file architecture, automatic PII redaction, and role-based access controls designed for community associations. Explore how TenantEvaluation supports HOA screening compliance.
Six Practical Steps For Secure HOA Applicant Data Collection
The six steps below form an operational sequence any HOA board or Community Association Manager can adopt. Each step closes a specific process gap that increases breach exposure.
- Build A Minimum-Necessary Data Inventory. The FTC Safeguards Rule at 16 CFR 314.4(c)(2) requires covered financial institutions to maintain a data inventory of the customer information they hold and where it lives. For HOAs, that inventory should map directly to what governing documents and screening criteria require: full legal name, date of birth, contact information, FCRA-required written authorization, employment details, and rental history. Notice what is not on that list. Social Security numbers are collected for background check consent and identity verification, and they do not belong in the board’s review materials. Every field beyond what screening requires widens breach exposure without adding compliance value.
- Adopt The Two-File Record Architecture. This framework gives HOAs a clear way to separate decision-making from sensitive data handling. Split every application into two distinct files: a decision file containing application status, approval or denial, the checklist tied to governing documents, dates, and the stated reason for the decision; and a sensitive screening file containing government IDs, financial documents, credit reports, and background check results. Volunteer board members access only the decision file. The authorized screener or management company handles the sensitive screening file. This separation keeps raw PII away from board members, reduces liability exposure, and simplifies access control.
- Enforce Role-Based Access Control For HOA Board Members. 16 CFR 314.4(c)(1) and (c)(5) require least-privilege access controls and multi-factor authentication on systems holding customer information. In practice, board members do not need access to an applicant’s credit report, and HOA volunteers have no permissible purpose for viewing Social Security numbers. Access should stay scoped to the decision file only so volunteers see decisions and reasons, not raw PII. MFA belongs on every account that touches any part of the screening workflow to reduce account-takeover risk. Access must also be revoked promptly when a board member rotates off. Lingering access after board turnover is one of the most common structural vulnerabilities in community associations, and delayed revocation reflects a process gap rather than a technology limitation.
- Write An HOA Applicant Data Retention And Destruction Schedule. 16 CFR 314.4(c)(6) requires covered firms to securely dispose of customer information no longer needed, generally within two years, and ties secure disposal to a documented retention policy instead of indefinite storage. The board should adopt a written schedule with a clear trigger, such as the end of the applicable statute of limitations or a defined regulatory requirement. After that point, the HOA securely deletes electronic records and shreds paper. ISO/IEC 27001:2022 Control 8.10 calls for deletion methods that render data unrecoverable, including secure overwriting for magnetic media, cryptographic erasure for cloud storage, and physical destruction for end-of-life hardware. The schedule should name who triggers deletion, which method applies to each storage type, and how completion is documented. Every record kept past its requirement increases the impact of any breach.
- Require Security Clauses In HOA Screening Vendor Contracts. 16 CFR 314.4(f) requires firms to select, contract with, and periodically assess service providers that handle customer information. Before signing with any screening vendor, the board should require the following clauses in writing:
- Confidentiality obligations covering all applicant PII
- Encryption standards for data in transit and at rest, with minimum TLS 1.3 and AES-256
- Access controls and MFA requirements on vendor systems
- Breach notification within a defined window, with the FTC requiring notification no later than 30 days after discovering a qualifying event under 16 CFR 314.4(j)
- Disclosure and approval of subcontractors with flow-down of the same obligations
- Defined retention periods and deletion methods aligned to the HOA’s own schedule
- Return or destruction of all HOA data at contract termination, with a certificate of destruction
With these clauses in place, the board can move to the final step of documenting the full workflow.
- Implement Secure Collection Mechanics And Document The Workflow. The collection channel itself must meet minimum technical standards, and the HOA should record the full sequence in writing. Applications should move through an encrypted portal using TLS 1.3 in transit and AES-256 at rest. FCRA-required written consent and e-signatures should be captured digitally on standalone authorization forms, not buried inside unrelated documents. Biometric identity verification, such as government ID validation combined with AI-powered liveness detection and facial matching, closes the gap between document-based review and confirmed physical identity. PCI Level 1 compliance sets the payment security standard for any platform that collects application fees. Automatic PII redaction keeps sensitive fields out of documents visible to unauthorized users. HUD’s April 2024 fair-housing screening guidance recommends that housing providers establish and consistently follow written screening criteria and log screening actions so there is an auditable record that every inquiry received the same treatment. The documented workflow should follow this sequence. The applicant submits through a secure portal, and the minimum required documents are collected. The authorized screener then reviews the sensitive screening file and creates a standardized decision record. The board accesses only the decision file through a role-limited dashboard. Records are retained per the written schedule, and deletion is executed and logged at the trigger date. Consistent documentation of this sequence forms a primary defense against both fair-housing claims and breach liability.
The Best Solution For Secure Applicant Data Collection In HOA Screening Compliance
TenantEvaluation is built specifically for community associations and management companies, with FCRA compliance built into its foundation. Founded in 2007, TenantEvaluation serves 5,000+ communities and processes approximately 100,000 applications per year, using direct reseller relationships with TransUnion and Equifax rather than third-party data scraping, and applying strict permissible purpose controls on every report.
The platform turns the playbook above into one enforced workflow. The two-file record architecture is built in, so the decision file and the sensitive screening file stay structurally separated and volunteer board members never touch raw PII. Automatic PII redaction removes sensitive fields such as Social Security numbers and banking details from uploaded documents. End-to-end encryption and PCI Level 1 compliance protect the collection layer. Every application carries a built-in audit trail with timestamped actions, and automated adverse action workflows keep the process aligned with FCRA requirements.
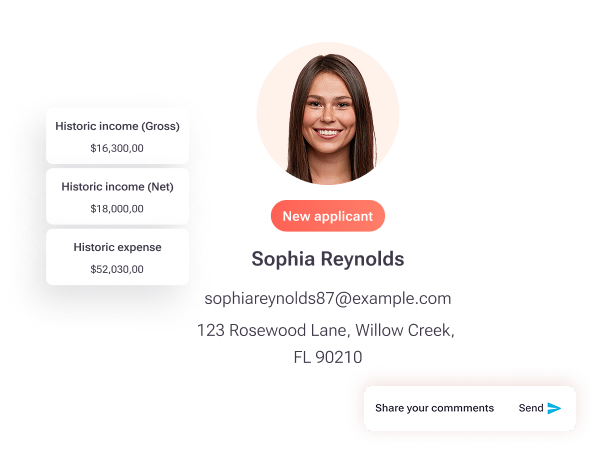
Key capabilities that enforce the compliance playbook directly include:
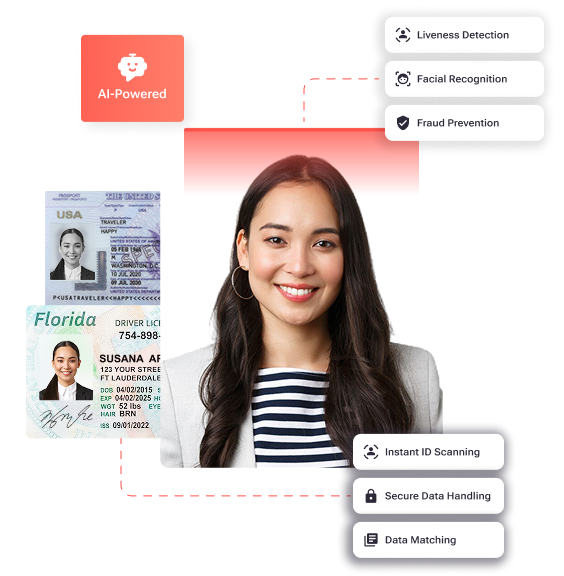
- IDVerify+ biometric identity verification embedded in the screening workflow, combining government ID validation, AI-powered liveness detection, and biometric facial matching to confirm applicant identity before approval decisions.
- QuickApprove an accelerated approval workflow with a board-ready review and voting dashboard, giving board members real-time access to the decision file without exposing the sensitive screening file.
- 55+ Communities Verification a built-in capability that helps Florida Condos and HOAs standardize age-restricted application handling, improving documentation consistency and reducing manual work.
- Lease Tracking centralized, real-time lease visibility and lifecycle control connecting resident onboarding, unit data, approvals, and lease documentation into one audit-ready workflow.
- TEpayments By Zinc a connected payment workflow that collects application fees and deposits during resident onboarding, with payments going directly from the applicant to the Association’s designated account while TenantEvaluation avoids holding funds.
The table below highlights where the compliance capabilities described above actually live across platforms. TenantEvaluation is the only option that states support for a two-file architecture and a board-ready dashboard, which matters directly for HOA screening compliance. Capabilities reflect publicly stated information as of September 2026.
| Capability | TenantEvaluation | ApplyCheck | Verify Screening Solutions |
|---|---|---|---|
| Built for community associations | Yes, FCRA compliance as foundation | No, background-check focused | No, background-check focused |
| Two-file record architecture | Built-in decision file / sensitive screening file separation | Not stated | Not stated |
| Board-ready voting dashboard | Yes, QuickApprove | No | Not stated |
| Biometric identity verification | Yes, IDVerify+ | No | Yes, vID |
Compare TenantEvaluation’s HOA screening workflow to your current process in a live demo.
Frequently Asked Questions
How Long Should An HOA Keep Applicant Screening Records?
As covered in step 4, records should stay only as long as there is a documented business or legal need. The practical question is what triggers deletion in your community. Many HOAs tie the trigger to the end of the applicable statute of limitations for housing-related claims in their jurisdiction or to a specific regulatory minimum. The board should record that trigger in a written retention and destruction schedule and log the deletion method and completion date for every record disposed of.
Can An HOA Board Member See An Applicant's Credit Report?
Under a properly implemented role-based access control framework, a volunteer board member should not have direct access to an applicant’s credit report. The FTC Safeguards Rule at 16 CFR 314.4(c)(1) requires least-privilege access controls, which limit customer information to people with a documented need for it. The two-file record architecture supports this requirement by giving board members access to the decision file, which contains the outcome and reasons, while the sensitive screening file with the credit report and financial documents stays with the authorized screener or management company.
Do HOA Volunteers Need Access To Social Security Numbers?
The minimum-necessary collection principle, reinforced by the FTC Safeguards Rule’s data inventory requirement at 16 CFR 314.4(c)(2), means access to any data field should be limited to those with a specific, documented need for it. Social Security numbers support background check consent and identity verification, which are handled by the authorized screener or a compliant screening platform. Volunteer board members have no permissible purpose under the FCRA for accessing raw SSN data, and the two-file record architecture keeps SSNs out of the board-facing decision file.
What Should An HOA Require In A Screening Vendor Contract?
The FTC Safeguards Rule at 16 CFR 314.4(f) requires firms to select, contract with, and periodically assess service providers that handle customer information. The clause set described in step 5 gives boards a starting checklist. In addition, boards should request a current SOC 2 Type II report or equivalent audit evidence before signing and should require the contract to spell out deletion methods and documentation, rather than relying on verbal assurances.
What Is The Difference Between An HOA Decision File And A Sensitive Screening File?
The two-file record architecture separates every application into two structurally distinct records. The decision file holds what the board needs to make and document an approval or denial, including status, the screening checklist tied to governing documents, the outcome, relevant dates, and the stated reason linked to written criteria. The sensitive screening file holds the raw PII and third-party data used to generate that decision, such as government-issued IDs, financial documents, credit reports, background check results, and biometric verification records. Board members see only the decision file through a role-limited dashboard, while the authorized screener or management company controls the sensitive screening file.
Conclusion: Turn The Written Process Into An Enforced Workflow
Most HOA applicant-data breaches trace back to ordinary process failures. The root cause is often a reused password, an unlocked storage location, or access that was never revoked when a board member left. A written, board-adoptable data-handling process that covers minimum-necessary collection, the two-file record architecture, role-based access with MFA and revocation discipline, a retention and destruction schedule, and vendor contract clauses gives the association a defensible position when a regulator, a homeowner’s attorney, or an auditor reviews it.
As noted above, TenantEvaluation was built for community associations with FCRA compliance at its core. The platform turns that written process into an enforced, audit-ready workflow with structural separation of decision and screening files, automatic PII redaction, built-in audit trails, biometric identity verification through IDVerify, and a board-ready approval dashboard through QuickApprove. Put this HOA screening compliance playbook into a live, enforced workflow with a TenantEvaluation demo.
